Two Chinese agents were charged with hacking U.S. computer systems from 2006 to 2018, in relation to a campaign across Europe, Asia and the U.S..
The U.S. Department of Justice (DOJ) and the FBI have identified the hackers as Zhu Hua and Zhang Shilong, both are members of a Chinese state-sponsored hacking group.
The hackers have been said to have obtained unauthorized access to computers of at least 45 entities, including commercial and defense technology companies and U.S. government agencies.
The hackers have also got their hands on personally identifiable information such as: names, social security numbers and phone numbers pertaining to at least 100,000 U.S. Navy service members.
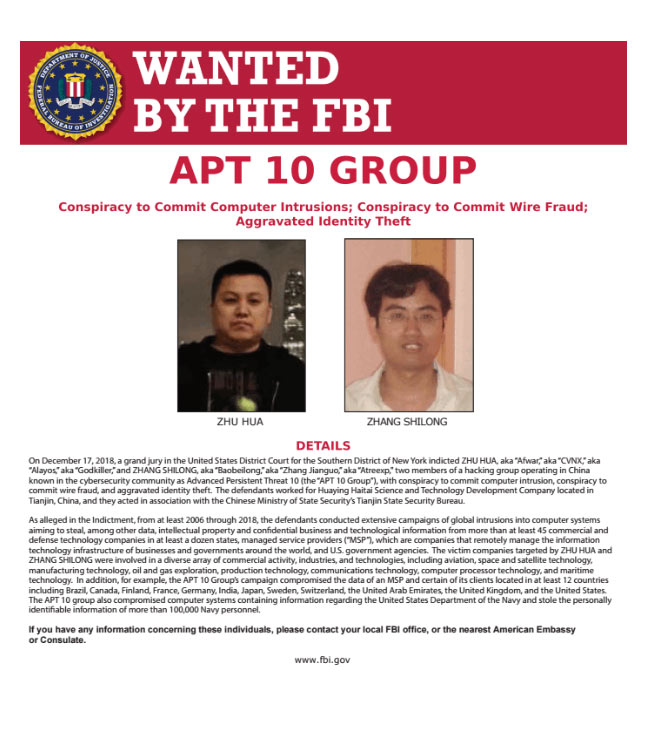
According to the unsealed documents:
The FBI, DOJ, and media outlets are characterizing the campaign as an intellectual property-theft (IPT) issue, alleging the Chinese agents’ intent was to steal technology plans.
The prosecutors accuse Zhu Hua and Zhang Shilong of acting on behalf of China’s ministry of state security to spy on some of the world’s largest companies by hacking into their outsourced systems which hold their email, storage and other computing tasks.
According to the FBI’s wanted poster for the group, known as Advanced Persistent Threat 10 (APT 10), or Cloudhopper, the group’s effort was massive:
"China’s goal, simply put, is to replace the U.S. as the world’s leading superpower and they’re using illegal methods to get there," said FBI director Christopher Wray at a news conference.
In response for this accusation, China’s foreign ministry said it opposed the “slanderous” accusations from the U.S. and other allies. It urged Washington to withdraw the accusations, saying that Beijing had lodged “stern representations” with Washington.
"We urge the U.S. side to immediately correct its erroneous actions and cease its slanderous smears relating to internet security," it said, adding that it would take necessary measures to safeguard its own cybersecurity and interests.
This case may further escalate tensions between Washington and Beijing after several repeated accusations between U.S. and China, as well as following the arrest of Meng Wanzhou, the Chief Financial Officer of Chinese telecommunications giant Huawei Technologies, in Canada at the request of the U.S..