It was first revealed by a Dutch independent software engineer Tijme Gommers. He discovered a vulnerability on McDonald's main website that essentially made it possible for attackers to steal sensitive user information.
Gommer explained the issue on his blog, saying that the flaws came from sloppy input sanitation present on the website. This enables hackers to steal login credentials as well as other sensitive information.
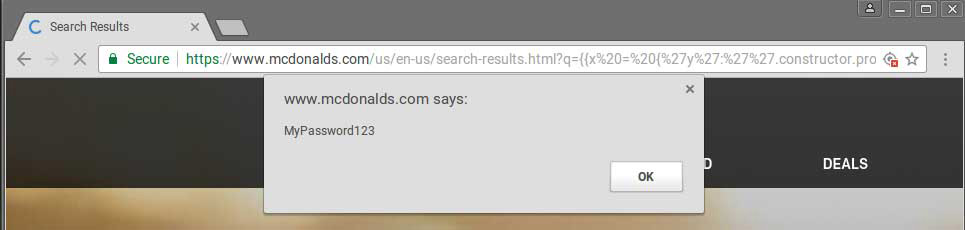
McDonald's website store user's passwords directly in cookies, instead of saving them on tokens. This makes it easy for attackers to recover the details by abusing the insecure cryptographic storage vulnerability and a reflected server cross-site-scripting vulnerability.
The flaw also eased Gommer in loading McDonald's external JavaScript files using a sandbox escape because the website uses JavaScript that can be loaded from another domain since it doesn't exclude it from using the Content-Security-Policy header.
The vulnerability affects those people who have previously signed up for restaurant accounts.
Gommers made attempts to report the issue to McDonald’s, but ultimately opted to disclose it on his blog after the franchise never responded to his inquiries.