Cybersecurity approach which relies on software, specifically software patches to vulnerabilities that have already been identified, is seen as not anymore reliable and not anymore ideal.
The Defense Advanced Research Projects Agency (DARPA) awarded $3.6 million grant to the University of Michigan. Here, a team of computer scientists and engineers that are developing 'Morpheus', an approach to hardware design capable of creating an unhackable computer.
Morpheus is one of several DARPA-backed projects, in a search for hardware cybersecurity solutions. It's a part of DARPA’s System Security Integrated Through Hardware and Firmware (SSITH) initiative.
"Security for electronic systems has been left up to software until now, but the overall confidence in this approach is summed up in the sardonic description of this standard practice as ‘patch and pray,’" said Linton Salmon, SSITH program manager from DARPA’s Microsystems Technology Office.
"Instead of relying on software Band-Aids to hardware-based security issues, we are aiming to remove those hardware vulnerabilities in ways that will disarm a large proportion of today's software attacks."
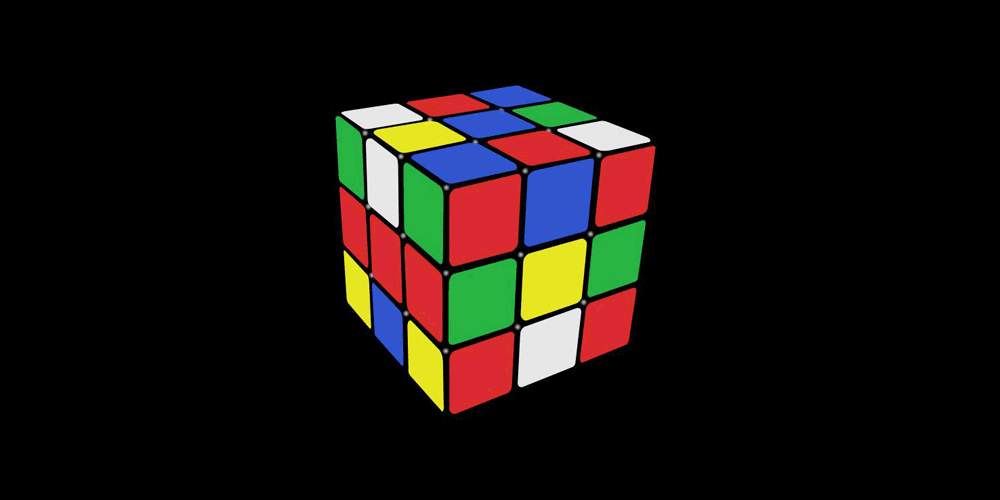
"We are making the computer an unsolvable puzzle," said Todd Austin, Morpheus team leader. "It’s like if you’re solving a Rubik’s Cube and every time you blink, I rearrange it."
The strategy could protect against future threats that have yet to be identified, a vulnerability that the security industry called a "zero day exploit."
"What's incredibly exciting about the project is that it will fix tomorrow's vulnerabilities," Austin said. "I've never known any security system that could be future proof."
DARPA wants protection against seven classes of hardware weakness, which include permissions and privileges, buffer errors, resource management, information leakage, numeric errors, crypto errors, and code injection. According to Austin, when Morpheus should be able to make those classes of attacks impossible.
To do this, Morpheus hardware design focuses on constant data movement, where information is moved and destroyed randomly and rapidly.
So if a cyberintruder discovers a bug or a weakness in a design, by the time the intruder designs a way to attack and take over the system, the data is already long gone and no longer in its original location. This is because the bug would constantly change and the location of the passwords would also change.
And even if an attacker were quick enough to locate the data, secondary defenses that include encryption and domain enforcement, would give additional roadblocks. The bug would still be there, but it wouldn't matter. The attacker won't have the time or the resources to exploit it.
This should prevent the intruder from retrieving any information necessary for a successful attack. The result, is a protection for both hardware and software.