At this time, the world has yet have detailed information about 'COVID-19' coronavirus vaccine. But hackers are trying to get ahead of that.
According to security researchers at IBM, they have found a global phishing campaign that targets organizations associated with the distribution of COVID-19 vaccines since at least September 2020.
In an announcement, analysts Claire Zaboeva and Melissa Frydrych of IBM X-Force IRIS said that the phishing campaign spans across six regions: Germany, Italy, South Korea, Czech Republic, greater Europe, and Taiwan.
The phishing campaign appears to be targeting the "cold chain" part of the supply chain.
It's through this segment that the vaccines are meant to be stored in -70°C temperature in order to remain potent.
This part of the supply chain is already having a challenge on its own, considering that it needs to keep millions upon millions of doses under extreme temperature, even while shipping them worldwide.
The campaign is said to focus on groups associated with Gavi, which is The Vaccine Alliance’s Cold Chain Equipment Optimization Platform (CCEOP) program.
The international organization that promotes vaccine access and distribution is working on the CCEOP to create the technology needed to keep the vaccines at very cold temperatures. Organizations involved with CCEOP include: the European Commission’s Directorate-General for Taxation and Customs Union, “organizations within the energy, manufacturing, website creation and software and internet security solutions sectors.”
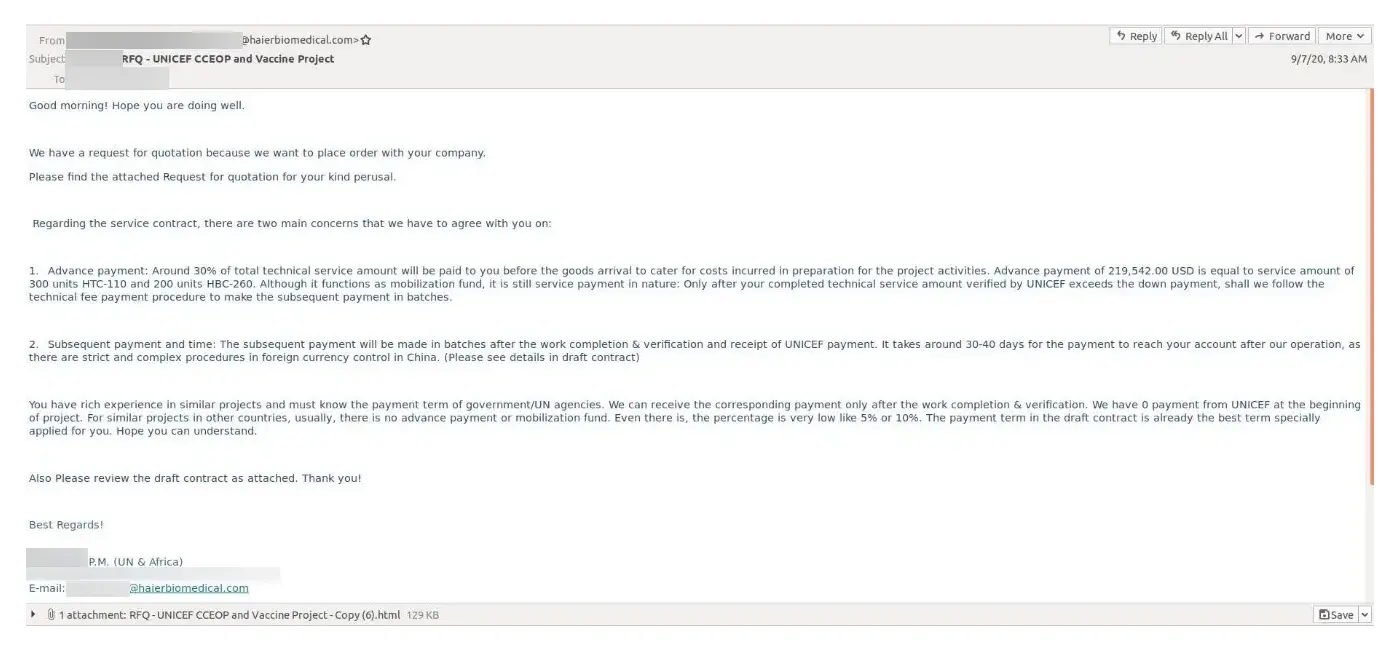
In the campaign, the malicious actors were found sending emails to the staff members at the organizations, claiming to be an executive from CCEOP supplier Haier Biomedical.
Through the emails, the malicious actors purportedly request quotations related to CCEOP, by including attachments that when opened, can be used to create backdoors for data extraction.
Successfully compromising a system, the malicious actors could steal credentials, or even gain unauthorized access to corporate networks to obtain sensitive information related to the COVID-19 vaccine distribution.
"IBM Security X-Force urges companies in the COVID-19 supply chain — from research of therapies, healthcare delivery to distribution of a vaccine — to be vigilant and remain on high alert during this time. Governments have already warned that foreign entities are likely to attempt to conduct cyber espionage to steal information about vaccines," the announcement reads.
At this time, the researchers at IBM have yet to know who is behind this campaign.
On the post, IBM recommends that companies and organizations involved in COVID-19 vaccine supply chain to “be vigilant and remain on high alert during this time.”
Following the announcement, the U.S. Department of Homeland Security's Cybersecurity and Infrastructure Security Agency (CISA) has issued an alert encouraging the organizations to review IBM’s report, "and recommended best practices to remain vigilant."
Hack attempts to organizations involved with COVID-19 vaccines aren't nothing new. With the whole world literally waiting for the vaccines, all eyes are on them.
Back in July, the U.S. and its allies have charged two Chinese hackers for stealing data from companies working on COVID-19 treatments. This happened following the U.S. accusations back in May, saying that China has been funding and operating hacking campaigns to steal vaccine research from the U.S..
The authorities from U.S., UK and Canada have also accused group associated with Russian intelligence services. And in November, Microsoft has also detected malicious activities from state-sponsored hackers in Russia and North Korea on companies working with COVID-19 vaccines.